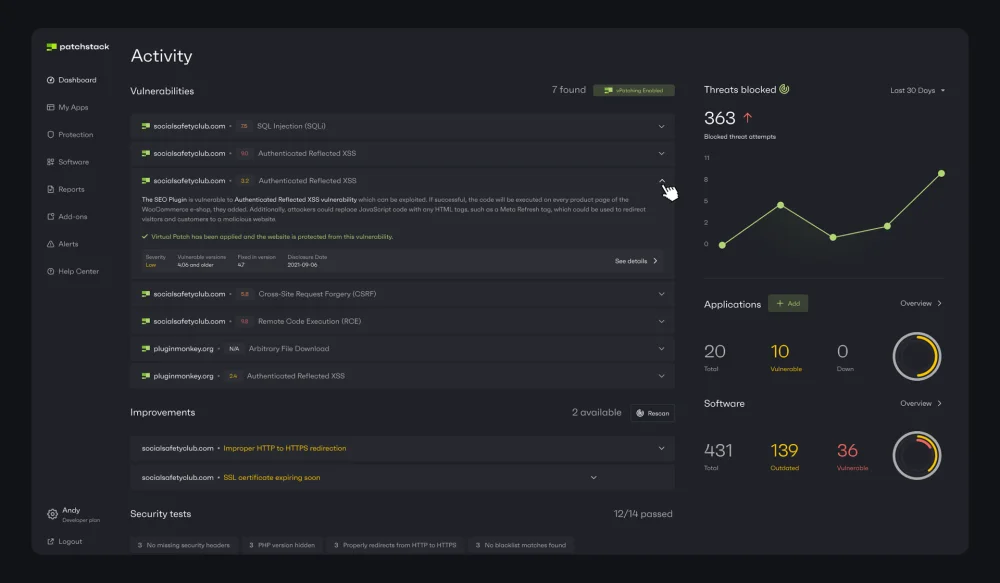
WordPress security research repeatedly shows that many vulnerabilities are found in third-party plugins and themes. The practical risk becomes much greater when administrators leave known updates uninstalled.
Plugins and themes need attention
WordPress itself is only one part of a site. Every plugin and theme adds code that must be maintained. Components that are no longer supported should be replaced, and unused plugins should be removed instead of simply deactivated indefinitely.
Updates should be timely
When a security update is released, delaying it can leave a known weakness exposed. Administrators should maintain reliable backups, keep an inventory of important components and have a routine for testing and deploying updates.
Security is a process
Strong passwords, limited administrator accounts, multi-factor authentication where available, current software and monitoring all reduce risk. Most of these measures are straightforward, but they work only when they are applied consistently.
Need help with your website or online store?
Describe your situation briefly and we will prepare a clear quote.
Request a quote